Behind the Contracts: Evidence of How the Definition of Legal Is Changing Across Industries
When an executive, clinician, or general counsel asks whether a practice is "legal," they are rarely asking a simple question. For decades, the baseline presumption was straightforward: an action was legal if it adhered to black-letter statutes, passed administrative muster, and avoided overt tort violations. Today, that definition has fractured. Across modern enterprises, a tool or workflow can be entirely permissible under statutory law yet create severe breach of contract exposure and uninsurable civil liability the moment private terms take effect.
This division between public regulation and private commercial risk is playing out vividly in healthcare systems. As detailed in a recent Medical Economics Report, the rapid introduction of ambient transcription software has forced physicians to confront a stark legal reality. While ambient listening tools comply with baseline federal privacy statutes, the accompanying vendor contract provisions routinely reassign malpractice and documentation liabilities straight back to the individual provider. What regulators consider legal on paper has become an active liability trap in practice.
📌 Key Takeaways:
- The Dual Framework: The legal definition and scope of corporate operations no longer rests purely on statutory compliance; it is dictated by the fine print of private commercial terms and risk-allocation mechanisms.
- Contractual Risk Shifting: Enterprise providers routinely satisfy broad regulatory mandates while assuming fatal indemnity obligations hidden inside standard software licensing schedules.
- Operational Burden: Institutional due diligence obligations now require continuous technical auditing, clear patient disclosures, and aggressive contract renegotiation before rolling out autonomous tools.
From Black-Letter Statutes to Private Contract Realities
The traditional understanding of legality separates law into neat compartments: criminal bans, statutory codes, agency oversight, and civil torts. If an enterprise did not violate an explicit code or regulatory standard, the activity was lawful. In modern transactions, that baseline is insufficient. An operational choice can clear federal hurdles while simultaneously exposing a business to complete financial destruction through private dispute mechanisms.
This divergence illustrates the growing rift between statutory law vs contractual obligation. Federal and state agencies write regulatory compliance standards to set universal floors for safety, privacy, and fair dealing. Private corporate agreements, however, bypass these general floors to construct individualized, enforceable legal regimes. A software deployment may satisfy every clause of HIPAA or the FTC Act, but the contract governing its use might strip away all implied warranties and shift third-party damages directly to the client. Legality, therefore, ceases to be an objective status granted by the state. It becomes an ongoing calculus of enforceability under modern law, weighed against the balance sheet of whoever signed the master services agreement.
How Clinical Ambient Agreements Shift Malpractice Risk
The practical fallout of this dynamic is visible inside medical examination rooms. Over 40% of outpatient health systems have piloted or adopted automated documentation systems over the past two years to alleviate administrative strain. Doctors routinely believe that using an enterprise-vetted digital assistant is entirely legal because the product holds third-party data certifications. What they miss is the underlying legal liability assessment.
Standard software contracts for clinical documentation place the entire burden of clinical accuracy on the end-user. When an automated ambient tool mishears a dosage, omits an allergy, or invents a clinical finding, the vendor's agreement shields the tech company behind sweeping indemnification clauses and disclaimers of fitness for medical use. The doctor who signs off on the record without spotting the discrepancy assumes 100% of the professional liability risk. The software company operates legally under commercial trade rules. The doctor, meanwhile, faces licensure sanctions and malpractice lawsuits because the clinical chart remains their sole legal responsibility. The technology vendor sells efficiency, but its paperwork offloads catastrophic civil liability.
Contractual Realities Across Enterprise Technology Deployments
The restructuring of legal exposure is not isolated to healthcare; it spans procurement, automated decision-making, and financial compliance. As enterprise software assumes greater autonomy, the allocation of liability has moved aggressively from developers to enterprise buyers.
| Operational Dimension | Traditional Legal Framework (2018, 2022) | Current Contractual Practice (2024, 2026) |
|---|---|---|
| Liability Allocation | Vendors carried mutual liability for software errors and gross negligence. | Unilateral indemnification clauses push all output accuracy risks to end-users. |
| Consent Protocols | General terms-of-service notices satisfied statutory notice thresholds. | Explicit, affirmative informed consent requirements mandated by state privacy rules. |
| Compliance Auditing | Periodic point-in-time security reviews (SOC 2, ISO certifications). | Continuous due diligence obligations covering algorithmic bias, data leakage, and drift. |
| Breach Exposure | Direct actual damages capped at 12 months of paid subscription fees. | Carve-outs leaving buyers vulnerable to uncapped third-party regulatory fines. |
Informed Consent and Due Diligence Under Modern Scrutiny
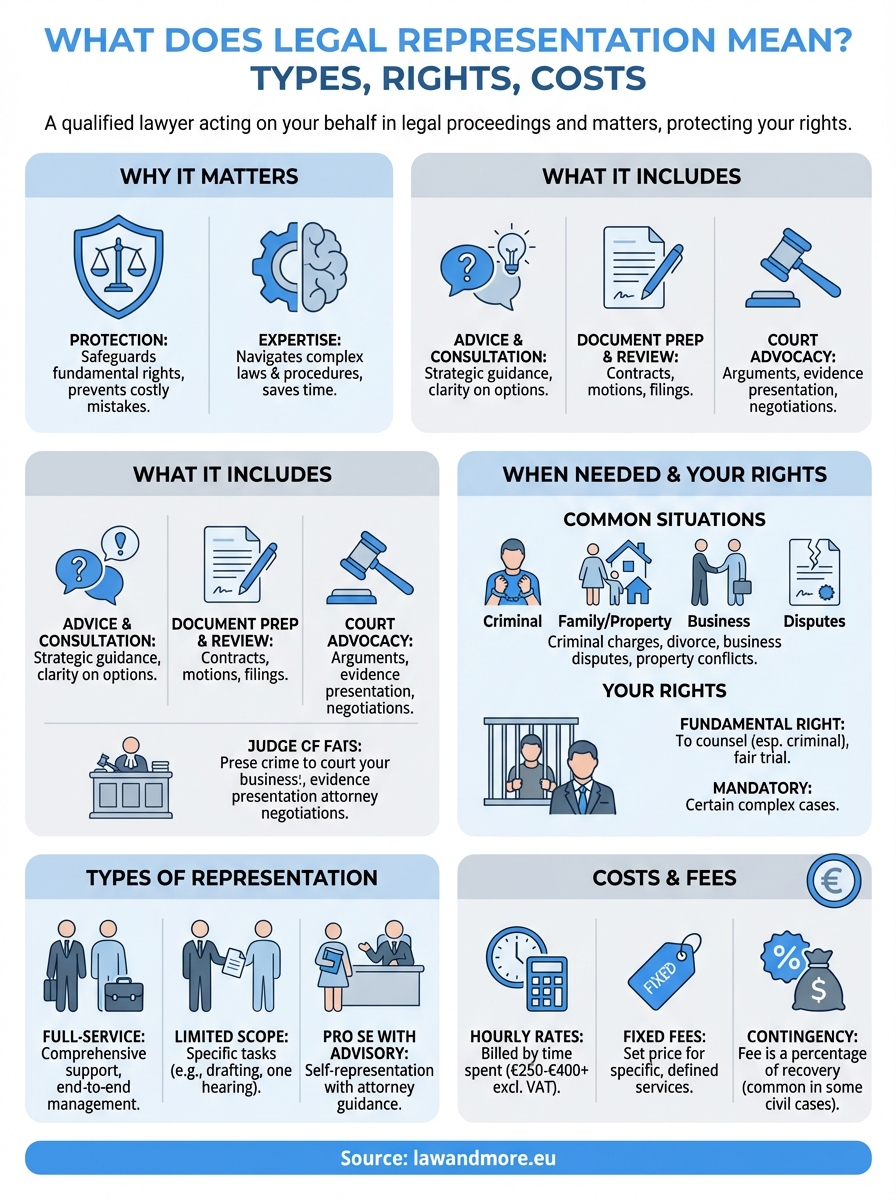
Operating legally once meant posting a static privacy policy or presenting a standard release form. That defense is dissolving. Modern courts and regulators now scrutinize the substance of user consent, particularly when automated tools record, analyze, or synthesize personal data.
In healthcare and finance, informed consent requirements demand granular clarity. Patients and clients must be told precisely which systems process their communications, whether audio is stored, and whether synthetic models train on their records. A clinic that runs an ambient scribe without explicit oral and written consent can trigger state wiretapping violations, common law privacy torts, and severe regulatory enforcement. The physician may believe they are simply adopting modern practice tools, but their failure to institute rigorous disclosure creates immediate exposure to civil claims that malpractice insurance policies increasingly exclude.
Regulatory Compliance Standards Versus Enforceability Under Modern Law
A persistent myth among corporate operators is that satisfying an administrative checklist provides a legal safe harbor. Compliance officers often rely on baseline checklists: achieving SOC 2 Type II status, filing required transparency disclosures, or maintaining an updated HIPAA business associate agreement. In court, checklists do not stop litigation.
Judges and arbitrators evaluate actual performance, reasonableness, and contractual enforceability. When a hospital faces a catastrophic misdiagnosis suit stemming from an automated summary error, demonstrating adherence to emerging technology governance frameworks will not insulate the provider. The court examines whether the doctor fulfilled their independent professional duty to verify the data. If the software contract disclaims all warranties of accuracy, the vendor walks away clean. The hospital is left holding full financial liability, discovering too late that regulatory compliance and practical civil defense are completely different battlegrounds.
Frequently Asked Questions (FAQ)
Q1: Does regulatory compliance automatically mean an organization is legally protected?
No. Regulatory compliance confirms only that an organization meets baseline government standards. It offers no protection against common-law negligence claims, private breach of contract actions, or indemnification claims arising from vendor agreements.
Q2: Why are indemnification clauses in software contracts so dangerous for buyers?
Indemnification clauses dictate who pays when a third party sues over a failure. Tech vendors frequently draft agreements where the customer promises to defend and hold harmless the vendor if the software generates inaccurate or damaging outputs, leaving the buyer solely responsible for damages.
Q3: What steps should organizations take before deploying automated tools?
Organizations must demand mutual indemnity, eliminate unilateral hold-harmless clauses, verify that professional liability policies cover automated tool workflows, and institute explicit informed consent processes for all recorded parties.
Strategic Takeaways for Enterprise Governance in 2026
Understanding what is legal requires looking past the promises of vendor sales pitches and the surface-level assurances of regulatory checklists. The true boundaries of liability are written in the unread clauses of commercial contracts, where risk is systematically moved from tech providers onto individual operators and enterprise buyers.
Organizations that wish to protect their balance sheets must abandon the assumption that vendor tools are safe simply because they are commercially available. Due diligence requires line-by-line review of indemnity terms, explicit consent workflows that hold up in court, and an unyielding recognition that human professionals retain full responsibility for the tools they deploy. In the current enterprise environment, legality is not a passive status you inherit; it is a defensive perimeter you must actively negotiate and enforce.


