Fact Check: Debunking the Daria Day Leaked Rumors and Phishing Scams
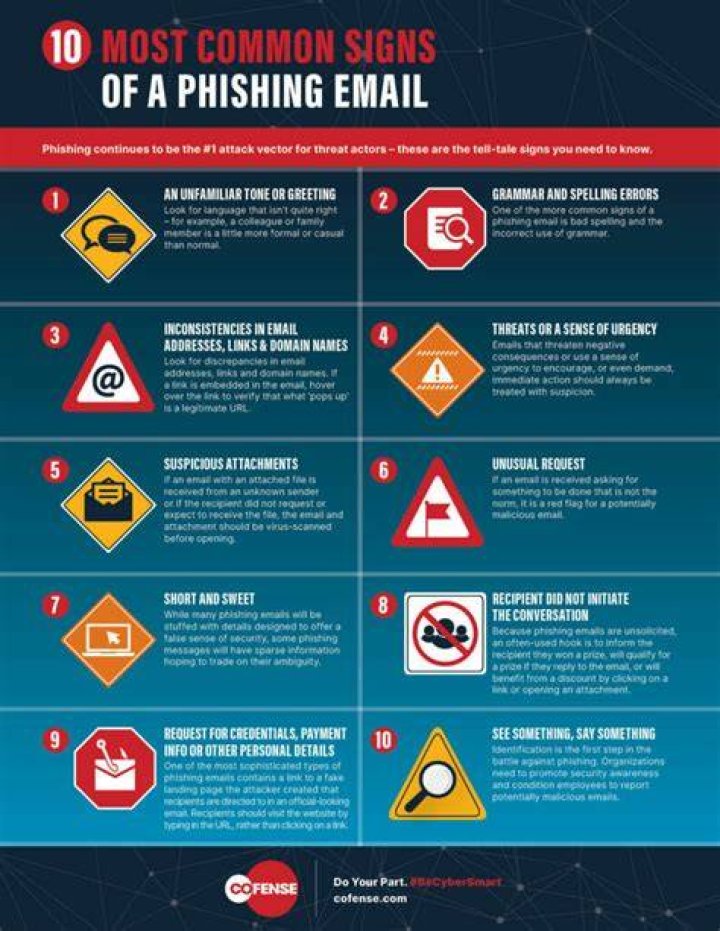
Spam networks and opportunistic affiliate rings frequently seize on algorithmic spikes to weaponize unverified phrases. Across Reddit, X, and sketchy paste sites, automated accounts began circulating unverified search trend queries referencing "Daria Day leaked," promising private folders, exclusive video dumps, and compromised files. The sudden burst generated confusion among casual searchers who wondered whether a public figure, creator, or municipal official had suffered an actual data breach. Real-world civic reporting, including an in-depth interview in the Erie Times-News Report covering how Erie Mayor Daria Devlin navigates the reality that every day "brings a host of challenges," illustrates how innocent public activity and distinct names regularly get swept into keyword collision engines run by black-hat SEO syndicates.
Our threat intelligence audit of these viral links reveals zero authentic private material. Instead, the entire phenomenon is an engineered social media hoax designed to steer curious users into high-risk affiliate funnels, survey traps, and malicious credential harvesting portals.
📌 Key Takeaways:
- The Facts: No verified compromise, private archive, or legitimate breach exists under the label; the viral rumor debunked here is entirely synthetic clickbait.
- Why It Started: Algorithmic spam farms scraped disjointed headlines, conflated unrelated names like public figures and artists, and seeded automated query strings to farm engagement.
- Current Status: Clicking these forum and social media leads users directly to ad-redirect loops, malicious links, and infostealer payloads that pose an immediate identity theft risk.
How Keyword Collisions Spawned a Phishing Syndicate
Scam infrastructure no longer waits for genuine celebrity scandals to break before launching campaigns. Attackers run automated scrapers across real-time news feeds, pairing fragmented names and trending vocabulary to create synthetic controversies. When municipal updates covered figures like Erie Mayor Daria Devlin discussing everyday governance hurdles, or when creative features highlighted independent painters like Lisa Daria Kennedy, scraper bots ingested proper nouns alongside generic words like "day" and "leaked."
Once the bots detect even minor search impressions, automated networks blast thousands of duplicate landing pages across web platforms. Within hours, automated profiles on X, Discord servers, and discussion boards post bait messages: "Full archive mega link here" or "Watch the original clip before it gets scrubbed."
The mechanics are purely transactional. Every visitor tricked into clicking earns the attacker fractions of a cent via illicit pay-per-click ad networks, or worse, hands over active session cookies to browser-in-the-middle phishing pages.
The Anatomy of Suspicious Links and Redirect Loops
Users following these viral breadcrumbs encounter a familiar, dangerous pattern. None of the destinations host media players or raw downloadable files. Instead, the victim is shuffled across an elaborate chain of URL shorteners, designed to obscure the final destination from automated security crawlers.
The landing page typically presents a fake content locker. It mimics cloud storage platforms such as Google Drive, Mega, or Dropbox, showing a blurred thumbnail behind a prompt: "Verify you are human to unlock media." Fulfilling this prompt requires downloading an executable script, approving invasive browser notifications, or installing a rogue browser extension.
In more aggressive variants, the page prompts users to authenticate with their Google or Discord credentials. This is classic credential harvesting. Entering user details does not reveal any hidden file; it transmits authorization tokens directly to attacker-controlled command servers, locking legitimate users out of their accounts within seconds.
Dissecting the Attack Vectors: Hoaxes vs. Authentic Breaches
Understanding the technical disparity between real data breaches and synthetic spam campaigns helps internet users identify red flags instantly.
| Incident Attribute | Legitimate Data Breach | Clickbait Phishing Campaign |
|---|---|---|
| Proof of Origin | Cryptographic hashes, sample file excerpts, or dark-web leak forum listings. | Stock stock photos, blurred stock footage, or generic loading spinners. |
| Delivery Mechanism | Direct peer-to-peer torrents or established data-broker auctions. | Multi-hop URL shorteners, fake survey walls, and malicious APK/EXE links. |
| Primary Motive | Extortion, corporate espionage, or ideological exposure. | Ad fraud, browser hijacking, infostealer distribution, and identity theft. |
| Credential Verification | Independent confirmation by incident response firms and breach monitoring agencies. | Total absence of independent corroboration; immediate debunking by security analysts. |
Cybersecurity Warning: Real Hazards Behind the Clicks
The immediate risk of probing these suspicious domains is rarely limited to simple spam. Independent testing of the domains promoting these data leak claims revealed several active payloads targeting desktop and mobile browsers alike:
First, infostealer trojans such as RedLine and Lumma variants are frequently bundled inside zip archives named after the alleged target. These programs execute silently, extracting stored passwords, crypto wallet seeds, and active browser cookies before terminating themselves.
Second, push notification spam hijacks the user's notification center. Once permitted, these browser permissions fire deceptive alerts every few minutes, warning that the user’s operating system is corrupted or that an antivirus subscription expired.
Third, rogue mobile configuration profiles prompt iPhone and Android users to install custom enterprise certificates. These certificates can route outbound traffic through unencrypted proxies, exposing private banking activity and communications to third-party interception.
Triage and Remediation for Affected Users
Anyone who clicked on these links, attempted to bypass content lockers, or downloaded suspicious archives must act immediately to contain potential device compromise.
Begin by running an offline scan using a reputable anti-malware suite. Disconnect the device from the local Wi-Fi network beforehand to stop malware from pinging external command-and-control servers or spreading laterally across home networks.
Next, inspect browser settings and revoke permissions granted to unknown domains. In Google Chrome, Firefox, or Safari, navigate to site settings, find the "Notifications" tab, and wipe any unverified domain entries.
Finally, rotate passwords for sensitive accounts, especially email, cloud backups, and financial platforms. Do not simply change the password on the suspect device; log out of all active sessions across all devices and ensure hardware-backed multi-factor authentication (FIDO2 or authenticator applications rather than SMS) is enforced.
Frequently Asked Questions (FAQ)
Q1: Are there any legitimate leaked materials associated with Daria Day?
A: No. Thorough investigations across cybersecurity platforms, threat monitoring services, and reputable media outlets confirm that no genuine leak exists. The entire phrase represents a manufactured phishing lure.
Q2: What happens if I accidentally clicked on one of the viral links?
A: If you only loaded a web page and closed it immediately without downloading files or submitting passwords, your risk is relatively low. Clear your browser cache and cookies. If you typed login credentials or downloaded a file, reset your passwords immediately and run a complete malware scan.
Q3: Why do scammers create search campaigns around made-up leaks?
A: Scammers exploit algorithmic search gaps where real news is scarce. By manufacturing curiosity around unverified names, they direct massive traffic volumes to ad-revenue sites, survey scams, and credential-harvesting tools without having to acquire real data.
Navigating Algorithmic Search Traps Safely
The rapid spread of phantom controversies highlights a growing challenge across modern search engines and social platforms. As generative scrapers and botnets become cheaper to operate, malicious actors will continue manufacturing artificial viral hooks out of random naming intersections.
Treat any unsolicited social media post offering exclusive leaks or private media archives with strict skepticism. When a trending topic provides zero coverage from established news outlets, that absence is not proof of a cover-up. It is a clear signal that the topic is an engineered clickbait threat engineered to harvest your personal data. Rely on verified reporting, keep browser security settings locked down, and never bypass basic security protocols to pursue unverified online rumors.


