What Does Proxy Mean? The Definitive Guide to Tech, Slang, Business, and Everyday Use
Strip away the technical jargon, and the definition of a proxy is straightforward: an authorized stand-in acting on behalf of someone else. The term originated from the Latin procurator, meaning an agent or manager, and entered Middle English as a legal designation for an appointed representative. While the root concept has remained unchanged for centuries, the practical implementation has splintered across radically different fields.
In 2026, the word appears everywhere from boardroom battles to network debugging. You encounter it when an enterprise employee configures an internal gateway on an iOS device, when pension managers vote on executive compensation, or when internet subcultures describe a coworker attending an in-person conference as a "meat proxy." According to research highlighted in an AIMultiple Report, mobile device proxy setups have surged among remote workers seeking to balance corporate network compliance with personal device boundaries. Navigating these overlapping applications requires looking past the single term to examine how delegation actually functions across technology, governance, and daily life.
📌 Key Takeaways:
- Core Principle: Across computing, finance, and law, a proxy is an intermediary given the authority to speak, route data, or cast votes for a primary actor.
- Network Mechanics: Proxy servers mask client IP addresses and filter traffic at the application layer, distinguishing them from operating-system-level VPN tunnels.
- Corporate Oversight: Shareholder ballots rely on proxy statements, where recent regulatory shifts have intensified fiduciary scrutiny on third-party voting advisers.
- Cultural Vocabulary: Modern vernacular uses "proxy" to describe physical surrogates in hybrid workplaces alongside historical practices like military proxy marriages.
Digital Intermediaries: How Proxy Servers Reroute and Mask Online Identity
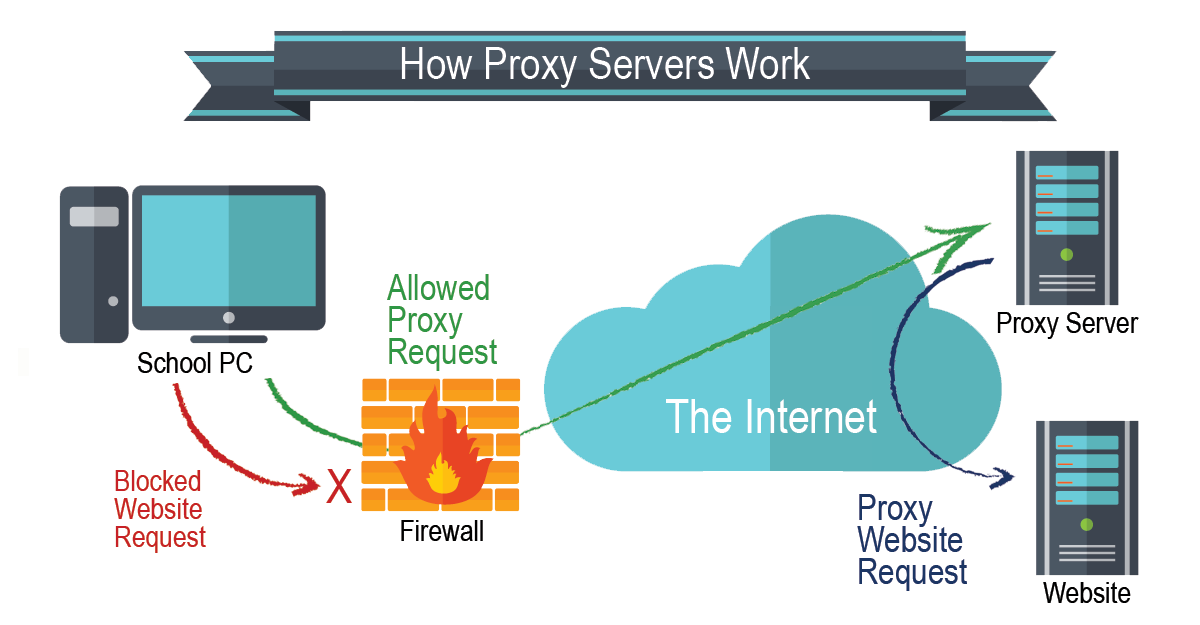
At its baseline, a proxy server definition describes an intermediary computer system that sits between a client application, such as a browser on your laptop, and the destination web host. When you send a request without a proxy, your machine connects directly to the target website, exposing your public IP address, approximate geographical location, and device metadata to the recipient server.
Routing that request through an intermediary server changes the communication path. Your computer sends the connection request to the proxy. The proxy reads the packet, strips or alters identifying headers, requests the data from the destination server using its own IP address, and relays the response back to your screen. This basic mechanism underpins two foundational architectures:
- Forward Proxies: Positioned in front of clients, forward proxies act as gatekeepers for outbound traffic. Schools and enterprise offices deploy forward proxies to enforce content security policies, block malicious domains, cache frequently accessed static resources, and enforce IP address masking for user privacy.
- Reverse Proxies: Positioned in front of web servers, reverse proxies protect the infrastructure behind them. Services like Nginx, HAProxy, and Cloudflare intercept inbound web traffic to distribute loads across server clusters, terminate SSL/TLS encryption, and prevent direct distributed denial-of-service (DDoS) attacks against origin databases.
Because the intermediary handles data routing at the application layer, frequently running over HTTP, HTTPS, or SOCKS5 protocols, it inspects traffic with high granularity. A company proxy can block specific URLs on social media platforms without cutting off access to the rest of the web. That targeted control makes proxies the workhorse of enterprise network gateway security, balancing internal auditing with perimeter defense.
Everyday Hardware: Managing iPhone Proxy Configuration and Network Gateways
Configuring an intermediary server is no longer confined to server racks or enterprise system administrators. Mobile operating systems have made these settings directly accessible to end users. On Apple devices, adjusting network settings allows hardware to communicate smoothly with local development servers, private enterprise intranets, or institutional Wi-Fi filters.
As tracked by coverage in AppleMagazine and network diagnostic communities, manual network routing on mobile devices routinely solves connectivity hiccups on closed campus networks. Establishing an iPhone proxy configuration involves navigating to Settings > Wi-Fi, tapping the active network connection, and scrolling down to the Configure Proxy menu. iOS offers three distinct operational modes:
- Off: The default state. All device traffic bypasses local intermediaries and flows directly to internet gateways.
- Manual: The user enters the proxy server's specific IP address or hostname alongside the designated port number (commonly 8080, 3128, or 1080). If the server requires authentication, the user inputs credentials to permit outbound data packets.
- Automatic: The operating system downloads a Proxy Auto-Configuration (PAC) file via an external URL. The script tells the device which domains route through the intermediary and which connect directly.
Software engineers use these manual connections to pair mobile hardware with debugging tools like Proxyman or Charles Proxy, inspecting encrypted API calls directly from a handset. However, misconfigured proxy profiles remain a primary cause of silent network failures. If an office proxy server goes offline or changes its port assignments, an iPhone configured to wait for its handshake will fail to load websites entirely, even with full cellular or Wi-Fi signal bars.
Proxies Versus VPNs: Architectural Trade-Offs and Performance Metrics
The terms "proxy" and "VPN" (Virtual Private Network) are often treated as interchangeable in consumer marketing. They are not. Both tools facilitate IP address masking and bypass localized geoblocks, but they operate at different layers of the networking stack and execute fundamentally different security tasks.
A proxy functions primarily at the application layer (Layer 7 of the OSI model). It handles requests generated by specific programs, such as your web browser or a torrent client, leaving background background services to connect over your normal, unmasked IP. Furthermore, standard HTTP proxies do not encrypt the traffic passing between your device and the proxy server itself unless an HTTPS connection is explicitly enforced.
A VPN operates at the operating system and network layer (Layer 3). When activated, a VPN creates an encrypted tunnel that routes every single packet leaving your device, from system update checks to background messaging syncs, through an encrypted transport protocol like WireGuard or OpenVPN.
| Core Dimension | Proxy Server (SOCKS5 / HTTP) | Virtual Private Network (VPN) |
|---|---|---|
| OSI Operating Layer | Application Layer (Layer 7) | Network / Transport Layer (Layer 3) |
| Scope of Traffic | App-specific (browser, designated client) | System-wide (all outbound device packets) |
| End-to-End Encryption | Optional; dependent on SSL/TLS target | Mandatory across the full client-to-server tunnel |
| Typical Latency Overhead | Low (minimal cryptographic processing) | Moderate to high (constant packet encryption) |
| Primary Enterprise Role | Caching, content filtering, web scraping | Secure remote access to internal private subnets |
For web scraping, data collection, and low-latency testing, proxies remain the superior option. They switch IP addresses rapidly across residential pools without the processing overhead of total tunnel encryption. Conversely, for protecting sensitive credentials over unencrypted public coffee-shop Wi-Fi, a VPN provides systemic security that an unencrypted application proxy cannot match.

Boardrooms and Ballots: Shareholder Proxy Statements and Regulatory Oversight
Outside server infrastructure, the word proxy holds immense power in corporate finance. Under United States securities regulations, retail and institutional investors rarely travel to a company’s physical annual general meeting to raise their hands. Instead, they vote by proxy.
Public corporations file a detailed shareholder proxy statement, officially known as SEC Form DEF 14A, weeks ahead of annual meetings. This disclosure provides shareholders with critical operational data: executive compensation structures, board member qualifications, potential auditor conflicts, and controversial shareholder proposals. Investors then submit a proxy card or online ballot, granting a designated corporate representative the legal authority to cast their shares in alignment with their instructions.
Because large institutional asset managers hold shares across thousands of distinct public firms, evaluating every individual ballot item internally proved impossible. This dynamic created the multi-billion-dollar industry of proxy advisory services, led by firms such as Institutional Shareholder Services (ISS) and Glass Lewis. These agencies analyze corporate filings and publish vote recommendations directly to pension boards and hedge funds.
This reliance on third-party voting firms has triggered aggressive regulatory intervention. According to legal analysis published by Mayer Brown regarding Department of Labor (DOL) guidance, federal regulators have instituted heightened oversight on retirement plan proxy voting. The DOL rules reinforce that retirement plan fiduciaries governed by ERISA cannot reflexively outsource their votes or rubber-stamp proxy advisory recommendations.
Plan managers must prove that every vote cast, particularly those addressing contentious environmental, social, or governance (ESG) measures, serves the pure financial interests of plan participants rather than outside political agendas. Delegating voting authority no longer excuses fiduciaries from legal accountability.
From Altar to Avatar: Proxy Marriage, Legal Power of Attorney, and Modern Slang
The core mechanics of delegation extend into family law, military protocols, and corporate humor. In the legal sphere, personal presence is typically considered non-negotiable for major life milestones. Proxy marriage represents the rare exception.
A proxy marriage occurs when one or both participants cannot physically appear at their wedding ceremony and authorize an agent to stand in their place to sign documents and take vows. In the United States, Montana stands out as the only jurisdiction permitting double-proxy marriages, where neither party needs to be physically in the state, provided at least one partner is an active-duty military member or Montana resident. Armed services personnel deployed to combat zones rely on these statutes to secure spousal health coverage, military housing stipends, and legal rights when wartime service prevents an in-person ceremony.
Similarly, legal power of attorney documents establish healthcare proxies. If an individual becomes incapacitated due to illness or trauma, a designated healthcare proxy carries the durable legal authority to approve surgeries, decline invasive interventions, or make end-of-life decisions according to the patient’s preexisting wishes.
Meanwhile, internet subcultures and corporate corridors have adapted the word into modern vernacular. The phrase "meat proxy" spread rapidly across remote-first tech organizations between 2024 and 2026. In distributed teams where 90% of staff work from home, a "meat proxy" refers to the lone local employee designated to walk into the corporate headquarters, sit in a physical conference room, plug in the meeting room microphone, or collect physical mail on behalf of their digital-only team members. It is humorous, self-deprecating slang, yet it mirrors the exact functional architecture of an intermediary server: a physical node handling localized real-world interactions for remote actors operating miles away.
Frequently Asked Questions (FAQ)
Q1: Does using an internet proxy keep my online activities completely anonymous?
No. While an intermediary server hides your home IP address from the websites you visit, the owner of the proxy server can log your unencrypted browsing activity, source IP, and timestamps. If you route sensitive traffic through a free, unverified public proxy, you expose your unencrypted data packets directly to third-party interception.
Q2: What is the main difference between a forward proxy and a reverse proxy?
A forward proxy sits directly in front of client devices to protect, filter, or mask user outbound connections to the wider web. A reverse proxy sits in front of backend web servers to protect hosting infrastructure from DDoS attacks, compress content, and distribute incoming traffic evenly across internal databases.
Q3: Why do corporate shareholders receive proxy statements before annual meetings?
Securities regulators require public companies to issue proxy statements (DEF 14A) to give all investors transparent information regarding board nominations, executive pay, and shareholder resolutions. This information allows investors to cast an informed ballot by mail or digital portal without traveling to the company’s physical headquarters.
Q4: Why does my home internet fail after turning on a manual proxy on my phone?
If you manually specify an IP address or port in your mobile network settings and that destination server becomes unreachable, drops offline, or rejects your authorization credentials, your device will continuously wait for a handshake that never occurs. Disabling the manual proxy or toggling the configuration back to "Off" restores direct web traffic.
Navigating the Mechanics of Modern Delegation
The definition of a proxy never shifts, even as its practical applications span across technology, finance, and law. At every step, the principle remains constant: inserting an authorized intermediary to act when direct access is impossible, inefficient, or unsecure.
Understanding the difference between an application-layer proxy and an encrypted VPN tunnel prevents costly enterprise configuration errors and home privacy lapses. Recognizing how shareholder ballots translate into corporate board decisions demystifies how multi-trillion-dollar pension systems exercise their voting weight. Whether running diagnostic packets through an iOS terminal, watching corporate fiduciaries navigate revised federal voting frameworks, or sending a physical stand-in to handle a remote deployment issue, recognizing the mechanics of the intermediary ensures you maintain control over who speaks for you, and how your data travels.


