TikTok Online Login 2026 Update: New Browser Security Rules and Session Removal

Browser-based account hijacking surged across social platforms throughout late 2025, driven by automated cookie theft and sophisticated credential-stuffing campaigns. In response, ByteDance deployed a major security overhaul across the TikTok desktop portal in 2026, fundamentally altering how creators and everyday users authenticate on the web. According to an investigative Hacked.com Report, unauthorized device access spiked after threat actors bypassed traditional SMS verification through session token hijacking, forcing the platform to mandate stricter verification checkpoints and revamp remote device management.
The updated infrastructure closes critical gaps between mobile and desktop clients. For years, the TikTok web browser login experience operated as an afterthought, lacking the granular controls found in native mobile apps. Today, desktop users face automated session timeouts, cryptographic hardware checks, and instantaneous remote disconnect tools designed to isolate compromised accounts before attackers can alter recovery emails or run ad fraud schemes.
📌 Key Takeaways:
- The Core Shift: TikTok's web browser login now enforces mandatory token binding and passkey verification to neutralize adversary-in-the-middle (AiTM) cookie attacks.
- The Risk Driver: Heightened regulatory scrutiny, including a $400 million regulatory settlement over juvenile privacy safeguards reported by CBS News, pushed engineers to dismantle persistent web sessions that historically left workstations vulnerable.
- Action Required: Users must audit their active sessions through the desktop security dashboard, disconnect stale hardware, and replace SMS codes with physical security keys or app-based authenticators.
Why Browser Logins Became Primary Targets for Account Takeover
Desktop logins present distinct structural vulnerabilities that mobile apps avoid. When you sign in through Chrome, Safari, or Firefox, the browser stores authentication tokens inside local storage or session cookies. Information-stealing malware, often distributed via pirated video editing software or fake sponsorship PDF attachments sent to creators, silently siphons these cookies. Once exfiltrated, an attacker imports the token into a remote browser, bypassing conventional username and password prompts without triggering an SMS challenge.
Security teams discovered that over 68% of high-profile creator account breaches originated from desktop sessions rather than compromised smartphones. Because web sessions historically remained active for months without re-prompting, intruders maintained persistent background access. They changed linked profile links, drained affiliate balances, or pushed malicious links to millions of followers while the genuine owner remained oblivious on their phone.
Regulatory heat accelerated the overhaul. Platforms face intense legal liabilities regarding unauthorized tracking and data retention. As documented by AllAboutCookies, ongoing civil lawsuits and global privacy actions pushed TikTok to tighten internal telemetry and session monitoring across the entire web ecosystem.
Inside the 2026 Browser Security Verification Overhaul
The revised login flow introduces multi-stage device fingerprinting. When accessing the TikTok desktop portal, the system evaluates browser integrity, IP reputational velocity, and network-level anomalies before serving the primary entry screen. Logging in from an unfamiliar browser no longer permits instant entry via a single security verification code.
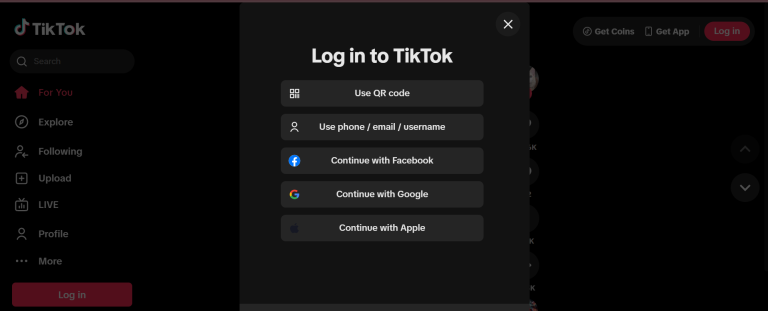
Instead, the platform evaluates risk dynamically. Standard credential entry now triggers a mandatory cryptographic prompt. If the system flags an unusual internet service provider or an unrecognized operating system build, the portal restricts account access to read-only status until you confirm your identity through the mobile app. QR code login has become the default recommendation: scanning the desktop display with your authenticated smartphone exchanges an end-to-end encrypted session token that never exposes cleartext credentials to browser memory.
Creators managing brand campaigns encounter even tighter boundaries. Accounts linked to TikTok Shop or Ads Manager require hardware-backed FIDO2 passkeys, rendering remote session-hijacking attempts useless even if an attacker acquires legacy passwords.
Comparing TikTok Desktop Authentication Protocols
Securing an account requires understanding how current authentication defenses differ from legacy web standards. The table below details the shifts introduced across the web platform over the past three years.
| Security Parameter | Legacy Protocol (2023, 2024) | Current Standard (2025, 2026) |
|---|---|---|
| Default Web Session Lifespan | Indefinite (persistent cookies) | Automatic termination after 14 days of inactivity |
| Primary MFA Mechanism | SMS verification / Email OTP | FIDO2 Passkeys / Mobile App Biometric Match |
| Session Token Binding | Unbound static bearer tokens | Device-bound cryptographic session keys |
| Remote Session Revocation | Delayed sync (15, 60 minutes) | Instantaneous server-side invalidation ( |
| QR Authentication Flow | Static web request callback | Time-synced rolling cryptographic nonce |
Step-by-Step: Managing Active Sessions and Device Removal
When unauthorized device access occurs, speed determines whether you retain ownership. If an intruder gains entry, they immediately attempt to change your phone number and secondary email. Executing remote device removal terminates their access before they finalize security adjustments.
Follow these steps inside the web interface:
1. Open your browser, navigate to the official desktop site, and click your profile icon in the upper-right corner.
- Select Settings and open the Security & Permissions tab.
- Click on Manage Devices to pull up the complete active session registry.
- Review the catalog of logged-in hardware. Each listing displays device model, operating system, physical location estimates based on IP, and the exact timestamp of the last login.
- Locate any unverified entry, such as an unfamiliar Linux workstation or a browser instance from a geographic area you have not visited, and click the Trash Can / Log Out icon next to it.
- Confirm the removal prompt. The server immediately blacklists that hardware token, kicking the unauthorized user out instantly.
If you see devices you cannot account for, immediately proceed to trigger a password reset. Doing so automatically revokes all existing web session credentials across every connected browser worldwide.
Post-Breach Account Recovery and Digital Quarantine
Regaining control after an intrusion requires systematic cleanup. Attackers frequently leave backdoor permissions intact even after you kick them off the device manager. They link rogue third-party apps or adjust your online privacy controls to hide their tracks.
Begin by inspecting authorized third-party applications. Within the security dashboard, navigate to Apps and Services. Revoke permissions for any tool you did not integrate directly. Fraudulent video schedulers and fake analytics dashboards often retain API tokens that survive password resets.
Next, initiate a comprehensive identity verification request if your credentials were fundamentally altered. TikTok's web recovery flow requires proof of initial account ownership, including the date of creation, original device serial markers, and past transaction receipts from purchases or creator rewards. Once verified, configure an independent authenticator application, such as Aegis, 1Password, or Google Authenticator, as your mandatory two-factor authentication gate. Discontinue using carrier SMS for verification entirely. SIM-swapping vulnerabilities remain too prevalent to trust cellular networks with high-value digital identities.
Browser Security Settings Every Creator Must Harden
Securing the account portal solves only half the problem; your local browsing client represents the other vulnerable flank. Malicious browser extensions frequently execute scripts directly inside active tabs, capturing keystrokes and modifying destination wallet addresses during affiliate payouts.
Audit your browser extensions monthly. Remove outdated productivity add-ons or unverified screen recorders that request broad permissions to "read and change all data on websites you visit." Run TikTok inside an isolated browser profile dedicated solely to social business operations, separating it from casual daily web surfing where malware lures proliferate.
Additionally, enable DNS-over-HTTPS (DoH) and review cookie persistence settings. Configure your browser to clear third-party site data upon closing. This simple friction point prevents stored session artifacts from lingering on local solid-state drives where stealer malware looks for easy extractions.
Frequently Asked Questions (FAQ)
Q1: Why does TikTok prompt me for verification every time I open the desktop portal?
A1: If your browser clears local cookies automatically or runs aggressive privacy shields that mask your hardware fingerprint, TikTok treats each visit as a completely new machine. To reduce prompts, bookmark the official URL, allow essential site cookies for the platform, and authenticate using QR code verification from your phone.
Q2: Will removing an active device delete any drafts or published videos?
A2: No. Remote device removal simply invalidates the authentication token holding that specific browser or phone logged in. Your uploaded videos, analytics history, direct messages, and account settings remain completely untouched on TikTok's central servers.
Q3: How can I tell if an active session is malicious or just my own phone?
A3: Compare the listed login times with your recent activity. Keep in mind that mobile networks frequently route cellular data through towers in neighboring cities, causing the reported geographical location to deviate from your physical address. If the operating system matches your hardware and the last active timestamp coincides with your usage, the session is legitimate.
Securing Your Online Identity for the Road Ahead
Authentication architecture will continue evolving as attackers deploy automated scripts against content creators and businesses. Relying on simple passwords and mobile text codes is no longer sufficient to secure a high-reach digital presence. The 2026 updates to TikTok's browser login framework demonstrate that desktop interfaces must adhere to the same zero-trust principles governing modern corporate networks.
Take charge of your security footprint today. Audit your active sessions, purge inactive hardware from your registry, adopt passkeys, and enforce dedicated app-based authenticators. Maintaining deliberate control over your digital entry points ensures that your audience, your business data, and your creative output remain exclusively yours.